Introduction
Hackers, crackers, cybercriminals… Unfortunately, the media and the general public have seized on these words for more than two decades. Words, like speech, a keyboard or a knife, are powerful tools that can be used for malicious purposes just as much as to “do good”.
Nowadays, as the means of communication develop and accelerate, the finish line in the information race has moved: it is no longer about finding the most relevant information or producing the best investigation backed by unshakeable evidence. No, today that finish line is driven more by “buzz” and speed: the winner is whoever publishes information as quickly as possible, even if that means skipping the actual work of a journalist.
What matters is no longer being the best, in terms of quality, but being the fastest. This trend, which began several decades ago, keeps accelerating day after day, speeding up “fake news”, shortcuts and approximations along with it. That broader subject will probably get its own post, but it lets me introduce a subject close to my heart: the indiscriminate abuse of the term “hacker” to refer to anyone and everyone.
A step back: who are hackers?
Well, to avoid launching into an explanation that could run to several hundred pages, I will start by revealing what they are not: cybercriminals. No, that is not a typo: hackers are not cybercriminals.
Let us put this urban legend to rest, a legend often spread by cybercriminals themselves when they call themselves “hackers”: no, there are no white-hat, black-hat or grey-hat hackers. No, there is no such thing as an “ethical hacker” either, any more than there are “unethical hackers”. For a hacker, a real one, ethics are not optional: they guide every single thing they do.
I know, you will reply that even “respected professionals” (in fact, usually “well-known professionals”, which is not the same thing; I will probably return to that in another post) now use the term “hacker” to refer to cybercriminals. And you have been reading that same definition for years in a press that, unfortunately, often does not know what it is talking about. On that subject, how many “computer worms” have been called “computer viruses” in the press or by “experts” invited onto BFM TV?
Yet reality is far, very far, from what you usually read or hear about the subject, whether in the media or, worse still, at supposedly professional conferences on it.
So I will be as clear as possible: no, hackers are not cybercriminals, and therefore no: they *never* illegally break into an information system they do not own, whatever their motivations.
Let that be clear: the people who do that are crackers. I will come back to them a little further down.
Summing up what a hacker is, at least in information and communication technology, takes just a few words: a hacker is someone passionate about how operating systems and networks work. Although they are often programmers, that is not a requirement.
Through their advanced knowledge in various fields, hackers often discover new vulnerabilities at different levels: network, system, application… But those discoveries *are not used against other systems*. A hacker can obviously stumble upon a vulnerability in a system they do not own, just as you can discover a problem on a bus or in a friend’s car.
To judge a tree’s quality properly, you must not rely only on its appearance or its fruit: you must also look at its roots. To understand hackers’ roots, we will take a small step back in time, to when the term “hacker” first appeared: not so long ago for some, an eternity for others…
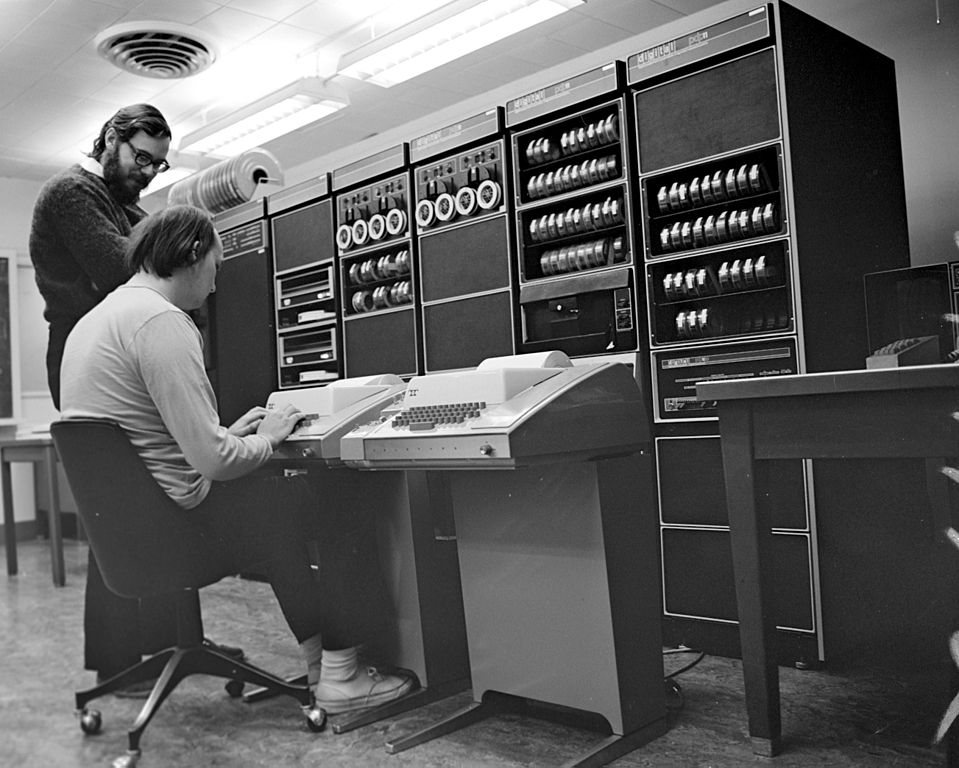
The story begins in the late 1950s at the famous MIT (Massachusetts Institute of Technology). It is the era when the first computers appear: cabinets often occupying several cubic metres. At night, the first “hackers”, mainly students fascinated by this “new arrival”, the computer, in their world, spend their nights coding, debugging and experimenting on these machines, constantly improving the way they work.
These enthusiasts soon become a community almost despite themselves, gathered under the same banner, one that is more about ethics than technology: “all information must be free”.
Hackers are not people who destroy things, but people who move the world forward: for example, the people behind the creation of the Internet, or operating systems such as Unix or Linux, can be considered hackers. Ken Thompson, Steve Wozniak, Dennis Ritchie and Richard Stallman are hackers.
So, contrary to what you find in some supposedly “underground” publications, where “hackers” are portrayed with a cigarette hanging from their mouth (when they are not completely drugged up), dirty hair and a beer can beside their desk (these days, a hood is often thrown in too…), real hackers reject *every form of dependence and submission* on principle, for the simple reason that it would then be a brake, an obstacle to their freedoms and their development.
Crackers (cybercriminals)
But then, you will ask, who are the people we hear about so often in the press? The ones who steal credit card numbers, take over our digital identities, create viruses or, worse still, can endanger millions of people’s lives? Well, those people are cybercriminals, known as crackers in English, meaning someone who deliberately compromises the integrity of an information system, generally, though not always, as there are exceptions, for malicious purposes.
A cracker can destroy or steal data, attack other systems, commit any other harmful act, or have different motivations and not be destructive. There are several categories and subcategories of crackers, or cybercriminals. Many like to call themselves hackers, which can confuse someone who does not know better. Others prefer the term “white-hat” hacker. Yet however different crackers’ motivations may be depending on the situation (interest, challenge, dare, revenge, money, contract, information), a cracker remains a cybercriminal.
A tiny minority of cybercriminals are exceptionally skilled: they approach hackers, which they sometimes used to be, in competence and passion. Some hackers do become cybercriminals: once they cross that boundary (mens rea, which I will return to), and for as long as they do not cross back, they stop being hackers and become crackers. Sometimes the reverse also happens, and a talented cybercriminal ends up “going straight” and becoming a hacker.
Ultimately, what fundamentally distinguishes a hacker from a cracker remains “mens rea”, meaning a “criminal mind”, a “guilty intention”. This mens rea is expressed in a Latin maxim: “Actus non facit reum nisi mens sit rea”, which means it is not the guilty act that makes an individual a criminal, but their mind: their intention to commit a crime.
Note that the overwhelming majority of cybercriminals have little to do with hackers: often with limited skills, they simply use automated exploitation tools, which are increasingly numerous and accessible today, in what is often a random search for potentially vulnerable machines. Hackers and talented crackers often call them “lamers” or “script kiddies”.
The most dangerous and talented crackers often have nothing in common with the near-autistic “little computer genius” hiding behind a screen that people imagine or that you see in TV series.
The weakest link in an information system’s “security” chain remains, above all, the human factor. More often, it is knowledge and exploitation of human weaknesses through Social Engineering (the art of influence and manipulation) that makes the difference, rather than possession of a few 0-day exploits, exploiting a vulnerability that has not yet been publicly disclosed. Knowing a little psychology and knowing how to inspire immediate trust with a simple phone call or in writing are then essential skills for a high success rate in penetrating heavily protected networks and information systems.
Finally, it is true that while an exception has never proved a rule, many rules have exceptions. These are the people who permanently straddle both worlds, the “GreyHats”, or “grey hats”, who are difficult to place in either category: cybercriminals or hackers?
However, note that these exceptions have not been relevant for many years. To understand how they could arise, and how they might even be the source of this confusion, we need to go back to the beginnings of the Internet, the heyday of BBSs and parallel networks such as GTI, when working on a Unix system was unthinkable for an enthusiast. That operating system was reserved for wealthy organisations able to afford THE machine and the Unix that went with it. Even after saving for more than a year, no “ordinary” person, however passionate, could seriously imagine acquiring such systems and thus learning how they worked. At that time, some hackers broke into computer systems, not to steal data or cause harm, but simply to study those systems and learn more about their possibilities and limits.
And while that motivation may indeed have been understandable, that era is over: since the advent of GNU/Linux and other free systems, and now the widespread use of virtualisation, anyone can either salvage a few old machines from a dump or buy them for next to nothing and set up their own lab, with networks, systems, routers and servers, to examine every part of how they work; or use one of the many free-software virtualisation solutions available to build their own “virtual security lab”.
There would be much more to say, probably enough to write a book… yes, several. But I hope this post will help restore, at least in a few people’s eyes, the truth about this fascinating world, where, unfortunately, as in many other fields, received wisdom and prejudice sealed the media “fate” of real hackers long ago…
Christophe Casalegno
You can follow me on: Twitter | Facebook | Linkedin | Telegram | Youtube
Leave a comment
Add a comment