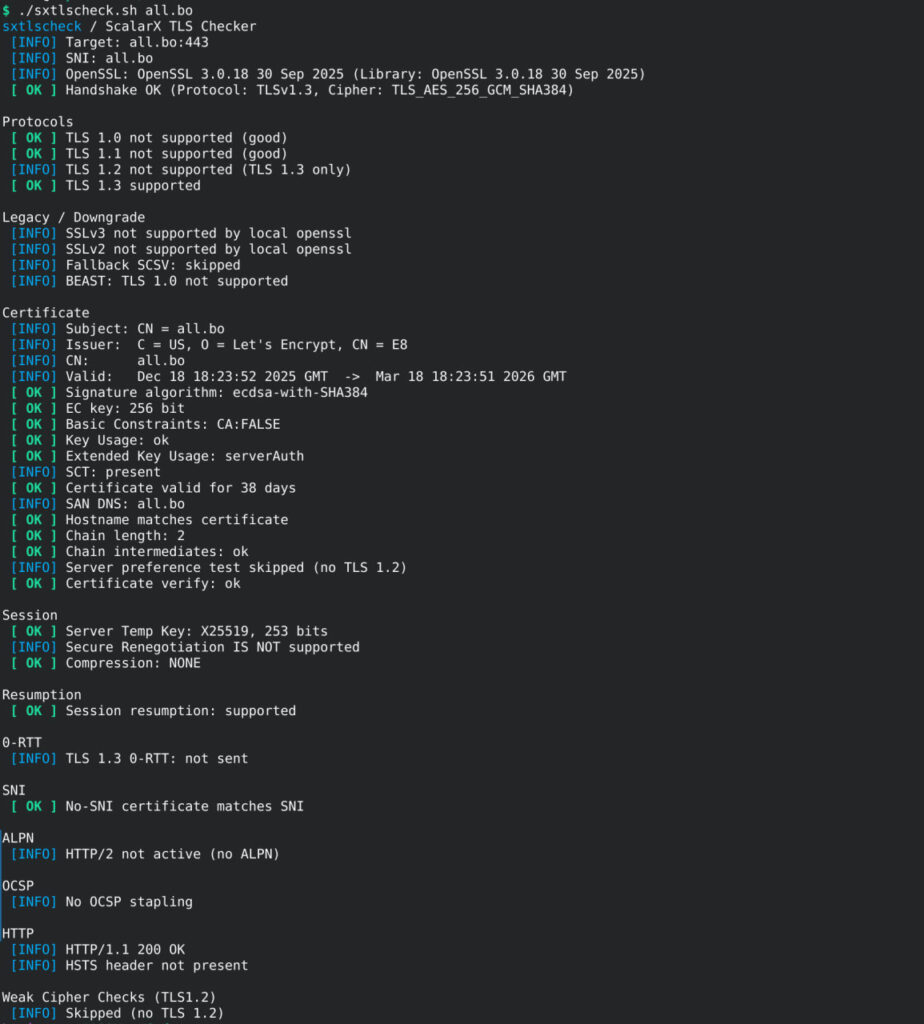
Good evening, friends, I am pleased to announce the release of SxTLSCheck (ScalarX TLS Checker). For context: when I needed to check certain aspects of an HTTPS service’s compliance or security, I previously used Qualys SSL Labs.
Then one day, (unpleasant) surprise: the test was no longer accessible (PS: it seems that it came back after several days of being inaccessible).
I am not trying to criticize them here, quite the opposite: this is another excellent service provided for free!
However, since I prefer to avoid depending on a third-party technical service when possible, I thought that migrating to an umpteenth web scanner was probably not the best solution for me.
I therefore set about writing my own TLS checker (in bash, of course!) with minimal dependencies (openssl) in order to keep control. It was also an opportunity to integrate these tests more easily into my StackX and ScalarX workflows. I also took the opportunity to implement the logic I need, with the corresponding alert levels, and to add a small function that will also let me integrate it into my internal certificate-expiration monitoring.
So, let me officially introduce SxTLSCheck (ScalarX TLS Checker), under the GPL license of course!
The objective is simple: quickly check the TLS/SSL compliance of an endpoint (host or URL) directly on your own machine, relying only on openssl s_client.
No online service, no exotic dependencies, no limitation on name / ip / port number, and not even any need for an internet connection: it works 100% locally!
PS: When I made this announcement on social networks, several people told me about testssl.sh, so I tested it, and it is an excellent tool, but I do not regret having written SxTLSCheck because it meets my specific needs better, is much lighter and can integrate directly into my stack and my current tool suite.
For those of you who want to know more, head here: SxTLSCheck
—
Christophe Casalegno
https://all.bo
Leave a comment
Add a comment